You can't attack a login page you can't load.
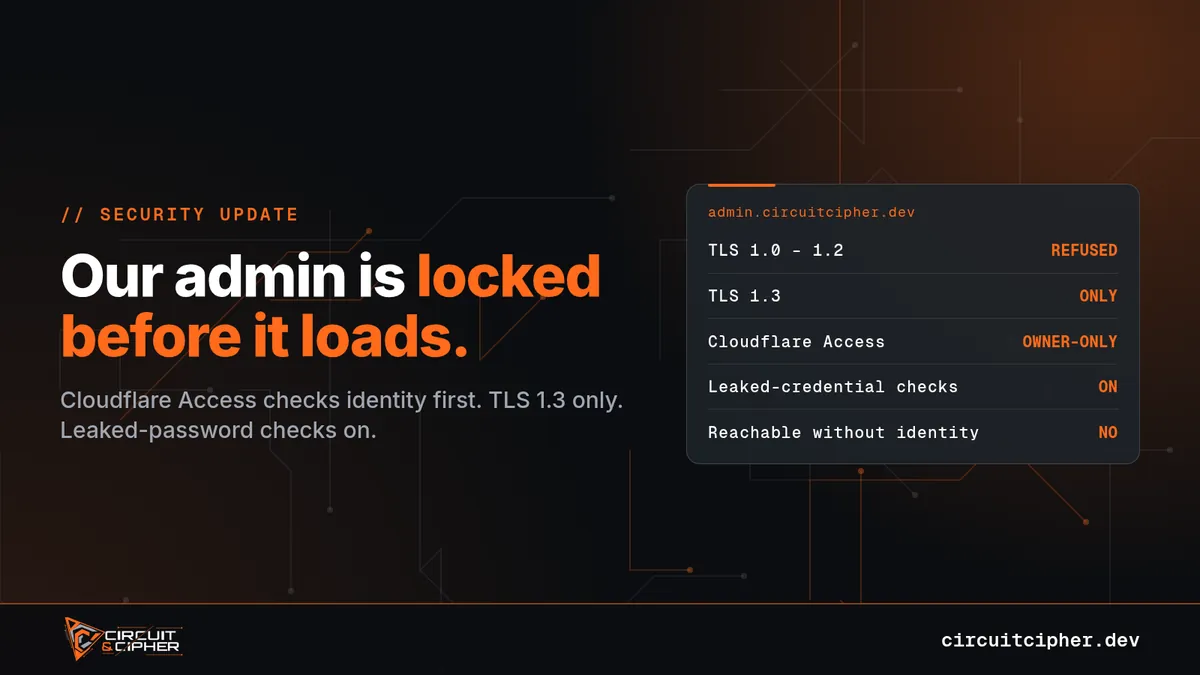
Our admin console sits behind Cloudflare Access: identity is checked before the app even loads. It refuses TLS 1.0–1.2, speaks 1.3 only, and leaked-password checks are on.
Small shop, serious security: circuitcipher.dev